

Security & DLP
Security & DLP is where you configure how Arbitex inspects and governs traffic — the policy chain that every request runs through, the policy packs and detectors that make up the 5-tier DLP pipeline (Tier 0: TF-IDF, Tier 1: Regex, Tier 2: NER, Tier 3: DeBERTa, Tier 4: CredInt), content filtering, email DLP, and the emergency kill switch.
What’s in this group
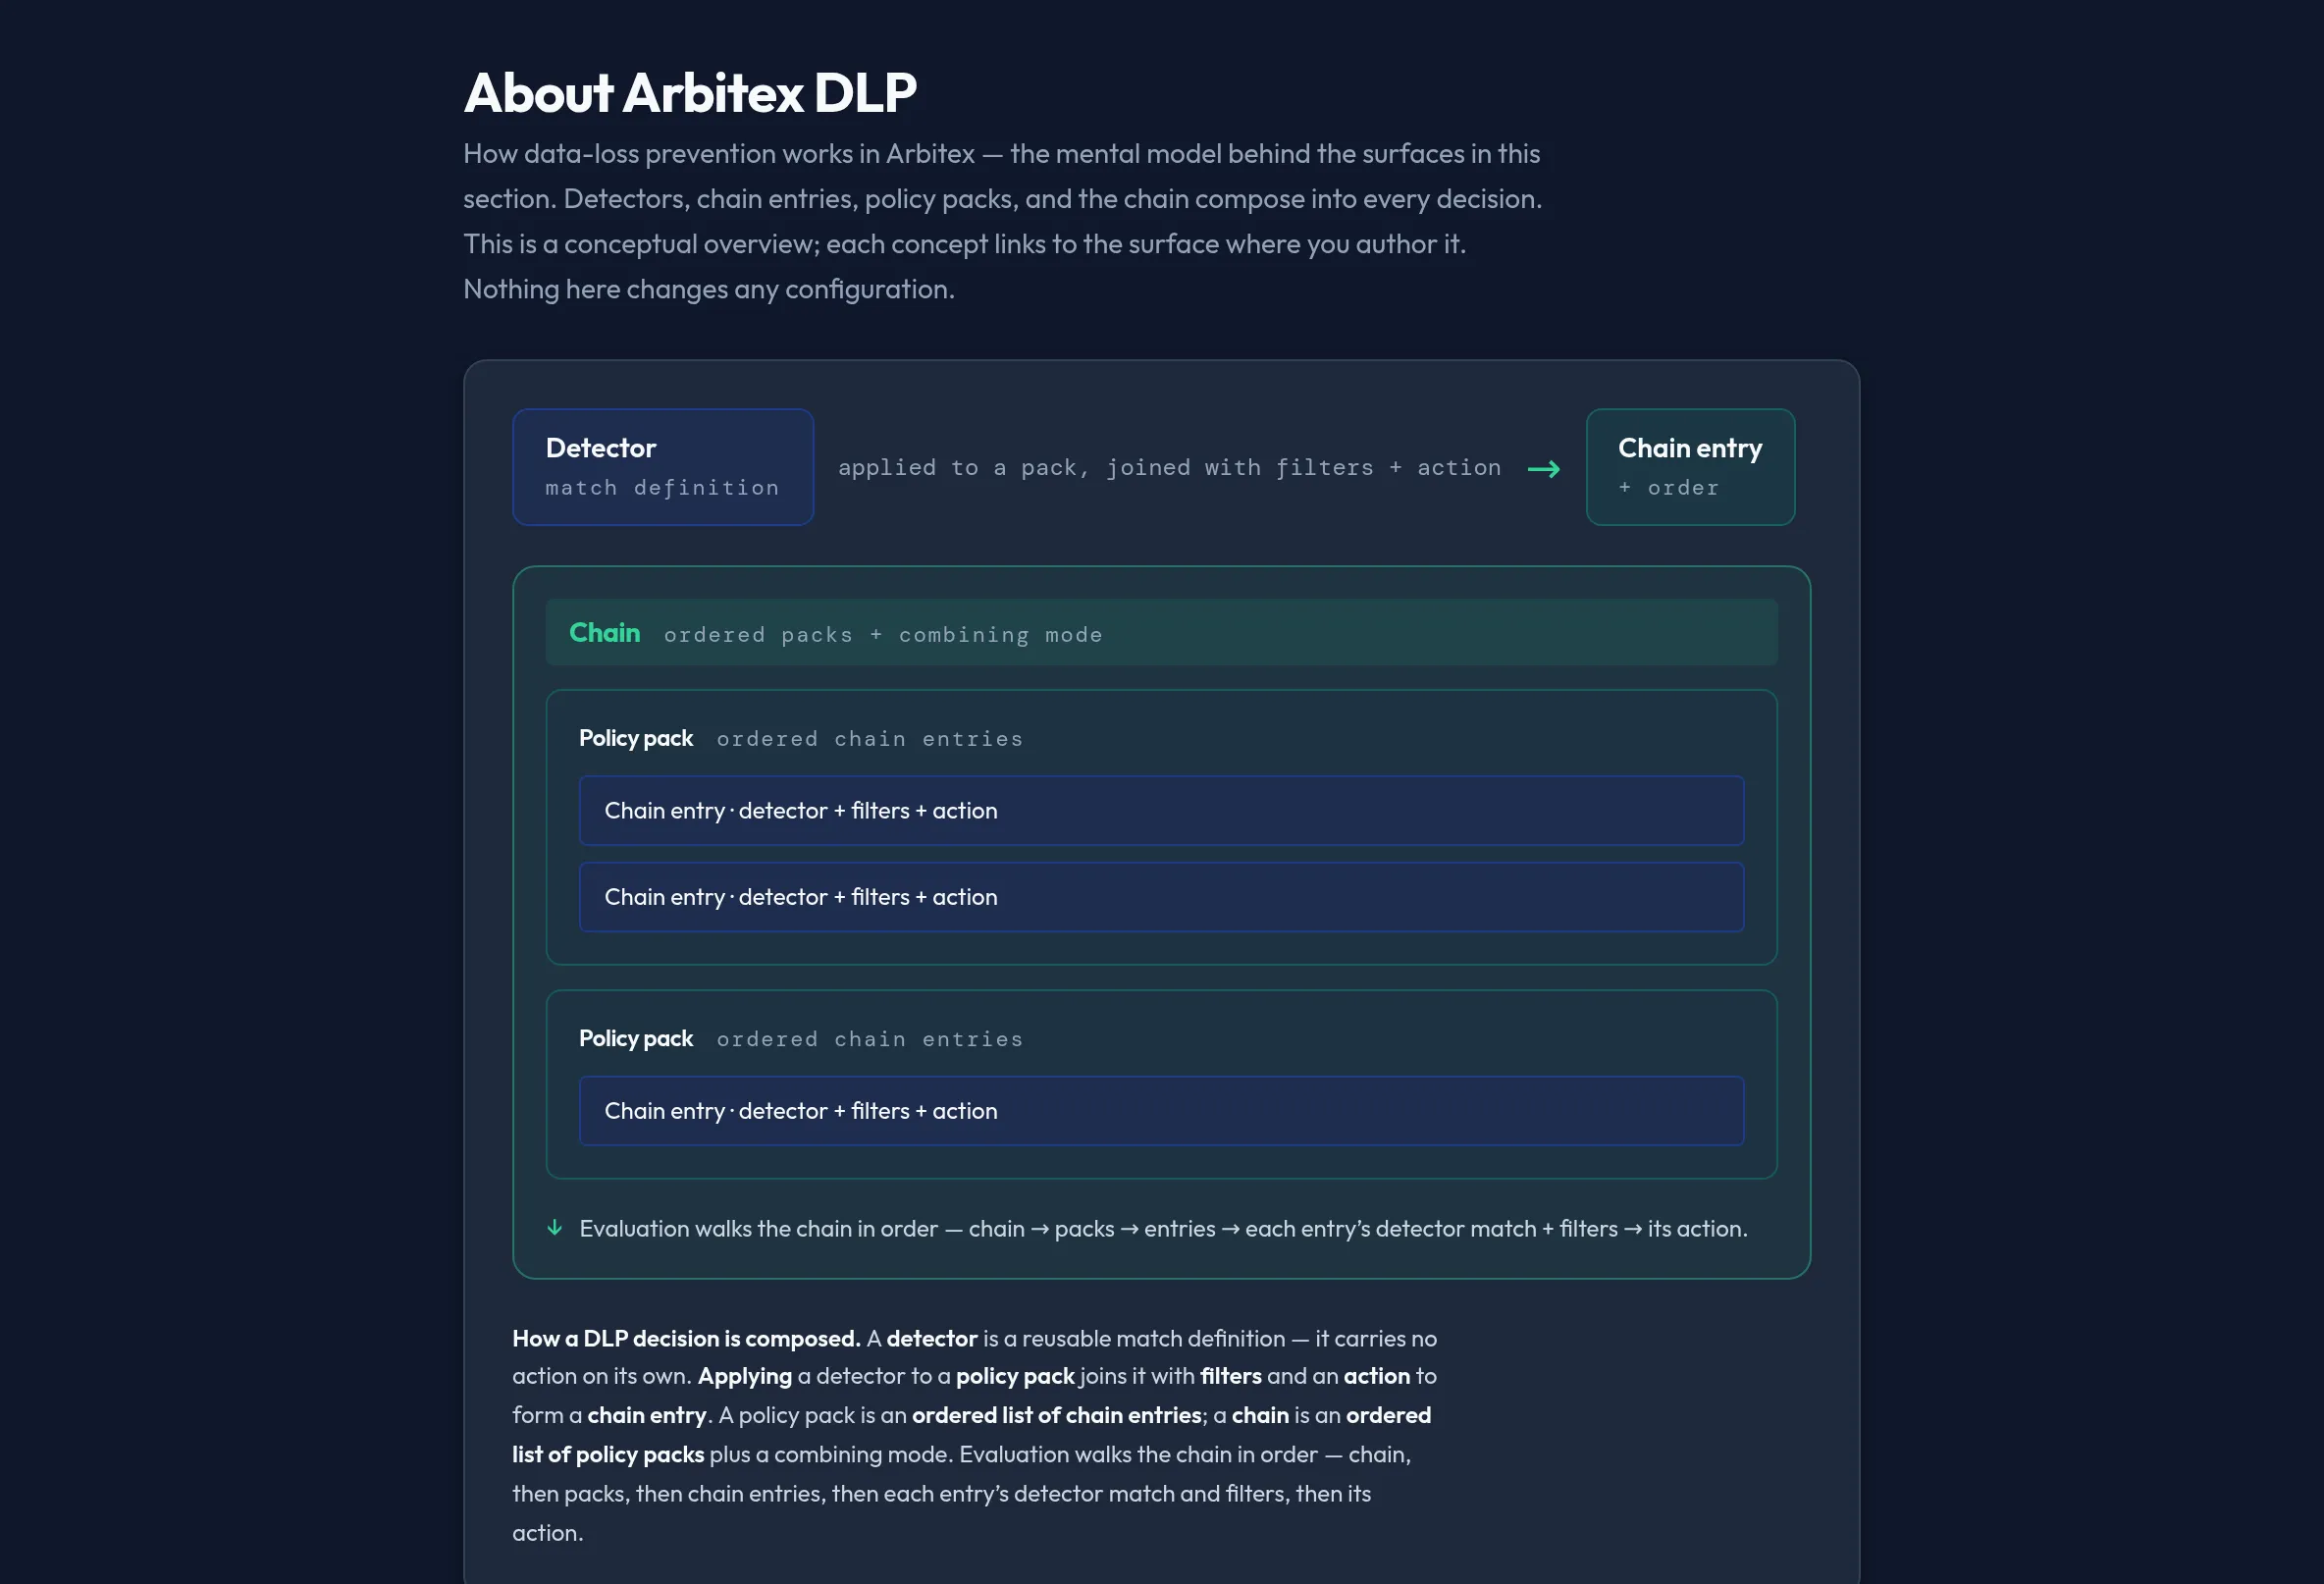
Section titled “What’s in this group”Each panel below maps 1:1 to a tab in the console’s Security & DLP group. Start with About DLP if you are new to the model — it explains how detectors, chain entries, policy packs, and the chain compose — then move to Chain and Policy Packs to author enforcement.
Related panels
Section titled “Related panels”KMS / BYOK has moved out of this group to System (key management is not a DLP concern). Compliance Matrix, Compliance Reports, and the DLP event history now live in Monitoring, alongside the rest of the console’s telemetry surfaces.
This group is also backed by a large body of existing reference documentation — API-level detail on the policy engine, the detection hierarchy, and compliance frameworks: